With EU product cybersecurity rules applying in stages, Advantech and DEKRA have announced a partnership to bring security reviews earlier into development, starting with an industrial edge system.
In an announcement dated Oct. 16, the companies said they had signed a memorandum of understanding to help manufacturers and system integrators address cybersecurity requirements during product design.
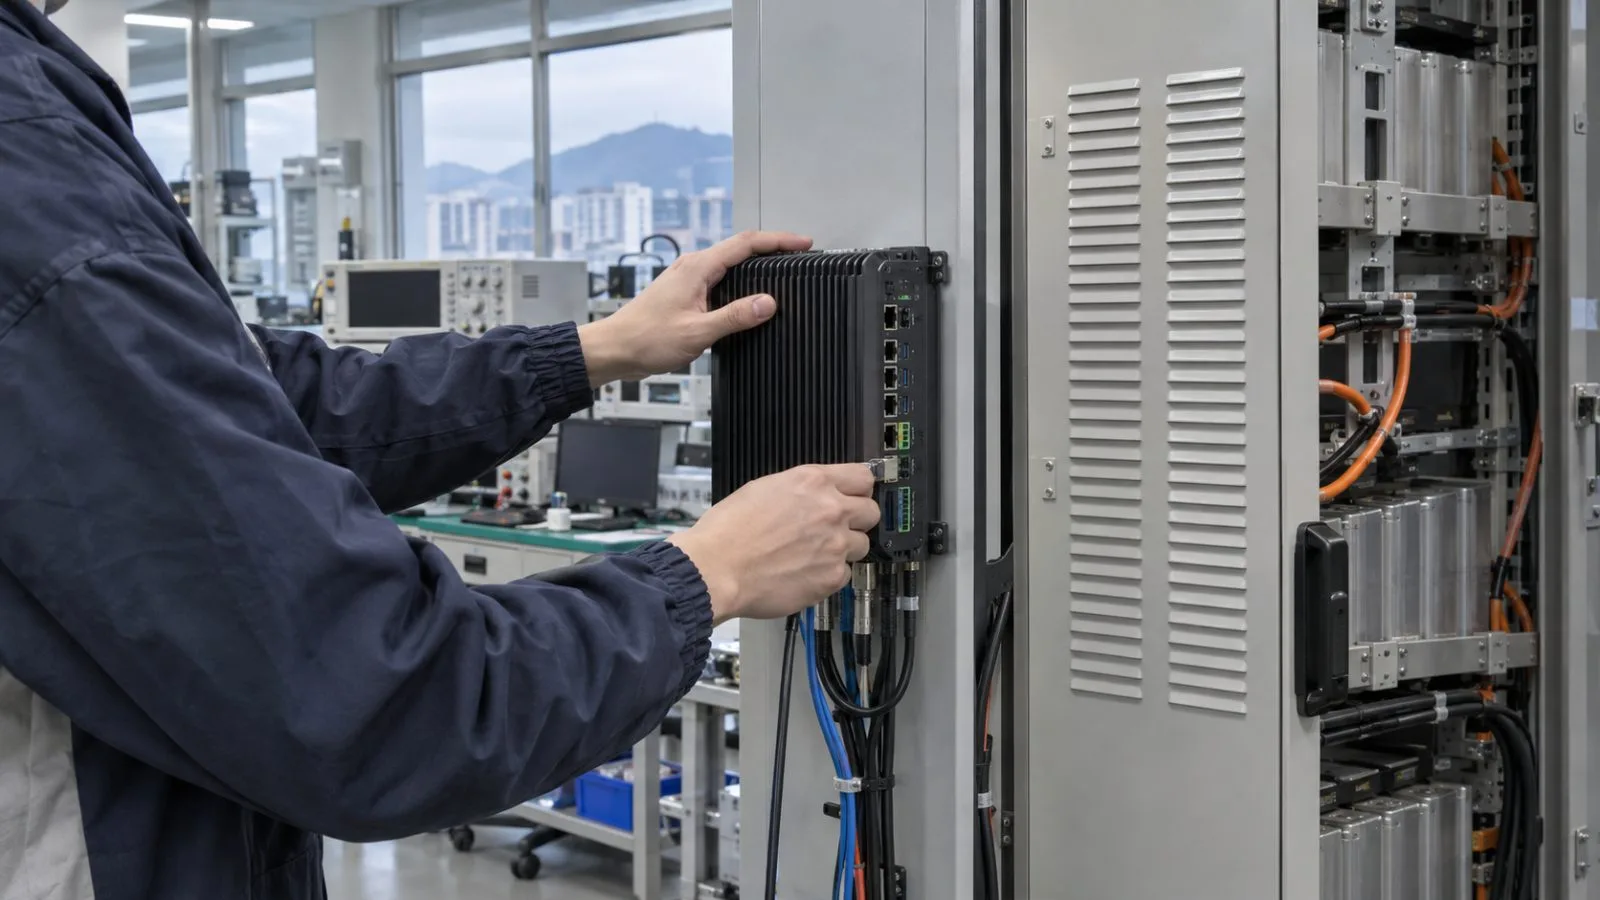
The first disclosed result is an Attestation of Conformity from DEKRA for security functions in Advantech’s AFE-E630 industrial edge system. DEKRA assessed those functions against IEC 62443-4-2:2019 Security Level 2 requirements. Advantech says the system is designed for commercial and industrial energy-storage management. The result is limited to the scope reviewed and is not described as confirmation that the system meets every requirement of the EU Cyber Resilience Act (CRA).
The MOU sets out work spanning preliminary technical reviews and feasibility studies, along with help preparing for certification. It also covers support for vulnerability management and secure-development processes. The companies expect to explore future work in energy equipment and transportation management, semiconductor production, robotics, drones and other mission-critical unmanned systems, as well as AI-enabled industrial applications.
Advantech said the collaboration is intended to help customers and system integrators identify relevant rules and cybersecurity gaps earlier in development. The company said that doing so could reduce the time and cost of design changes made later in a project; it did not provide a savings estimate.
The CRA establishes cybersecurity requirements for products with digital elements placed on the EU market. Its schedule is phased: Article 14 reporting obligations for actively exploited vulnerabilities and severe incidents apply from Sept. 11, 2026, while Chapter IV provisions on notifying conformity-assessment bodies took effect June 11, 2026. For product makers, those dates put some requirements more than a year ahead of the CRA’s general application date, Dec. 11, 2027.