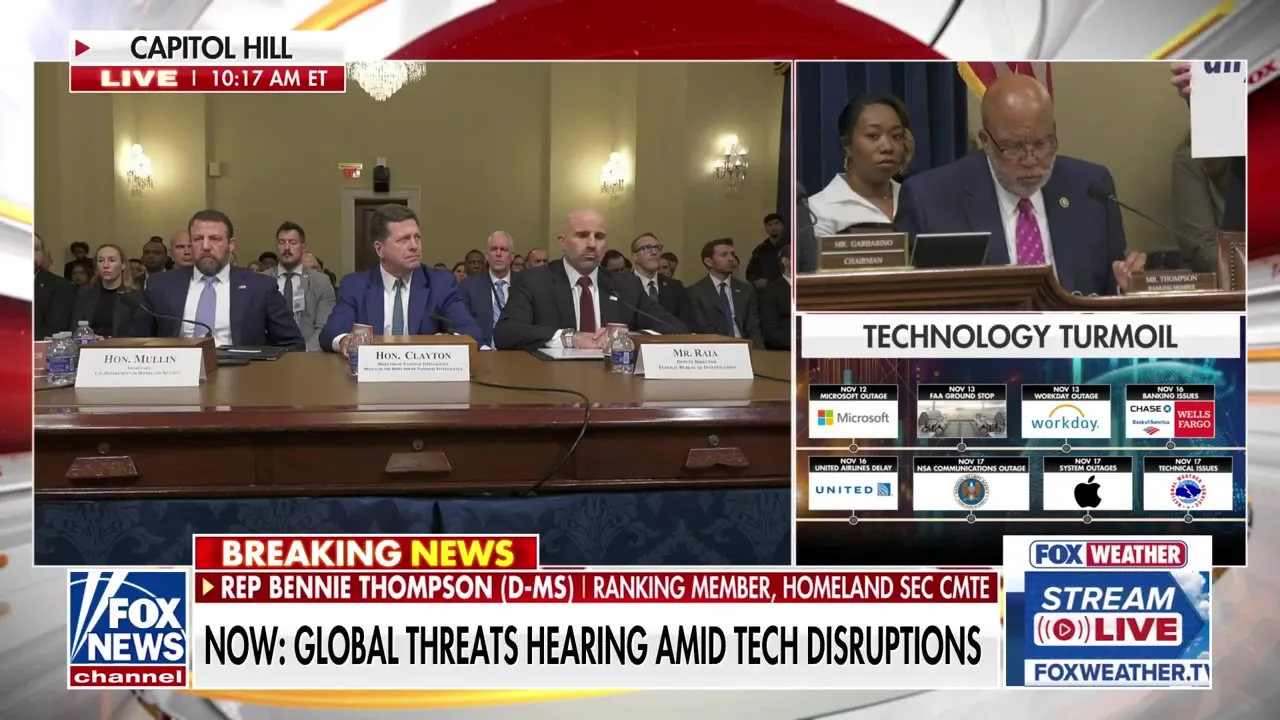
Iran-linked cyber activity has targeted U.S. critical infrastructure since the conflict with Iran began earlier this year, Homeland Security Secretary Markwayne Mullin told lawmakers, raising concerns about risks to essential services and the systems they rely on.
In written testimony to the House Committee on Homeland Security on Nov. 18, Mullin said Iranian government cyber actors and pro-Iran cybercriminals have increasingly focused on transportation, health care, water, energy and financial services since February. His testimony did not identify specific incidents, affected organizations or resulting damage, or explain how officials attributed the activity to Iranian actors.
Mullin said the operations have historically had localized and minimally disruptive effects against poorly secured industrial-control devices. He warned that vulnerable systems and weak cyber hygiene in lifeline infrastructure could create disruptive consequences.
Lawmakers also questioned intelligence and law enforcement officials about recent technology outages affecting airlines, banks and government operations. Director of National Intelligence Jay Clayton described the outages as separate incidents associated with maintenance and technical changes, and said they were not a coordinated or state-sponsored attack.
Federal Bureau of Investigation Deputy Director Christopher Raia said the bureau had found no indication of malicious cyber activity related to those incidents. The officials’ remarks did not connect the outages to Iran.