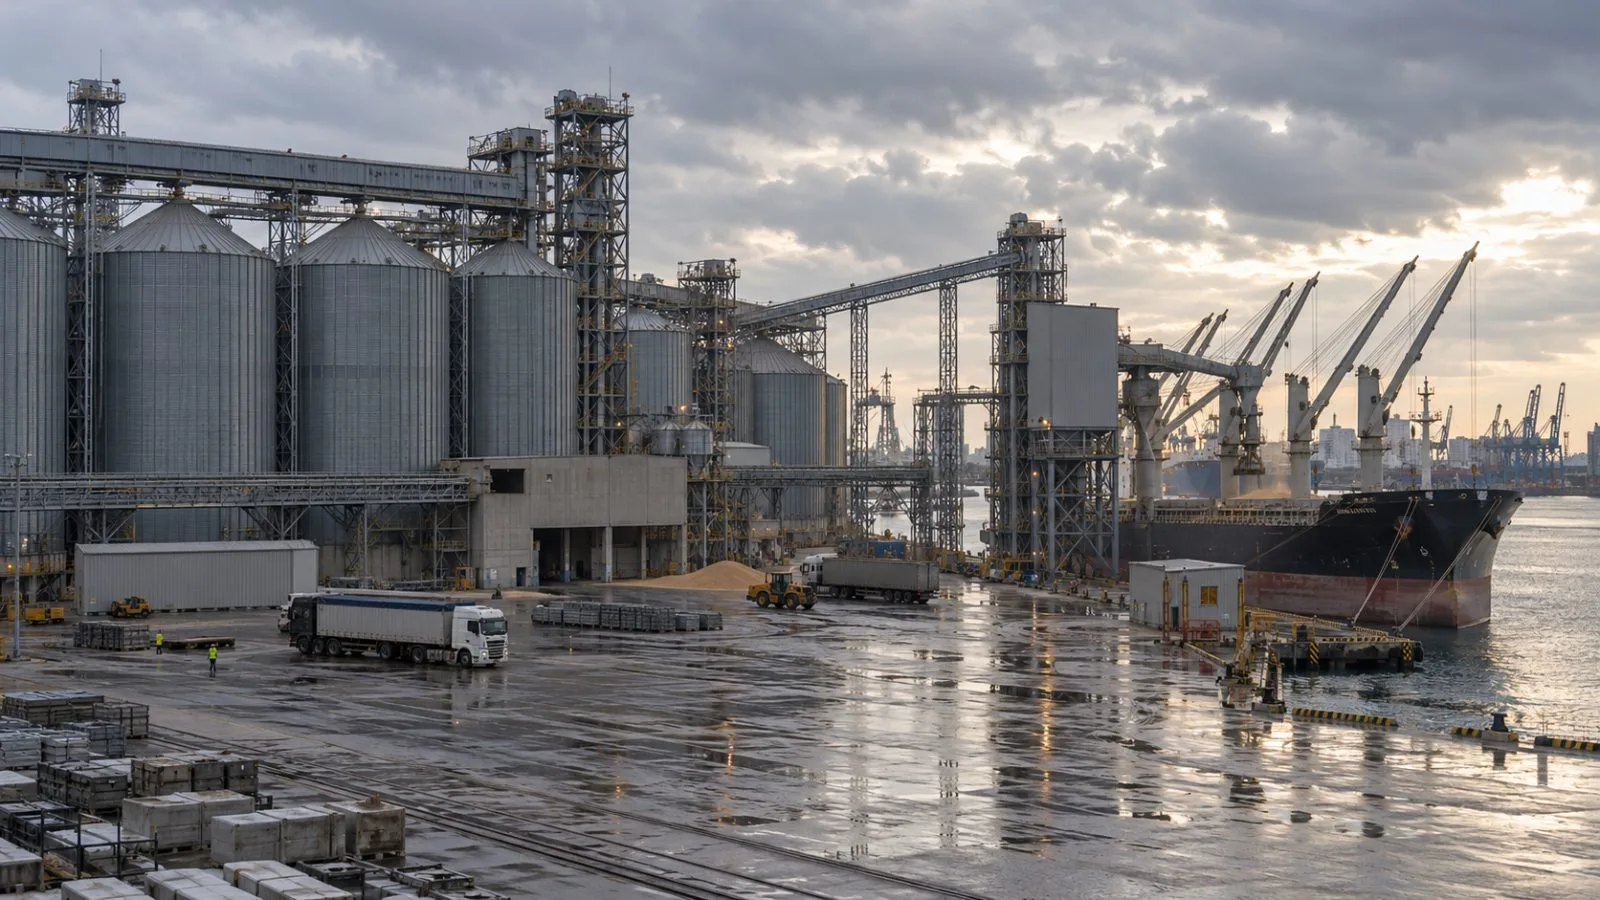
An attack on an unnamed Ukrainian grain logistics firm wiped data and used Yggdrasil for backdoor traffic, ESET told Reuters; the firm said it had not previously observed state-linked groups using the network.
ESET dated the intrusion to July 2025 and said it began after a phishing email reached the company, Reuters reported. The email was part of a campaign aimed at companies involved in logistics, grain handling and port operations across Ukraine. Research estimates cited by Reuters put agriculture’s prewar share at about one-fifth of Ukraine’s economy and almost half its exports.
Attackers installed software that gave them remote access to compromised machines, where they could inspect files, capture screenshots and copy out documents, Reuters reported. The program communicated through a server concealed inside Yggdrasil, an experimental mesh network run by volunteers without a central owner. ESET researcher Anton Cherepanov said the mesh setup made the traffic “harder to detect.”
Cherepanov said attackers triggered a data-wiping tool after securing administrator privileges. ESET identified the program as Microsoft’s SDelete, Reuters reported. A Microsoft spokesperson said the utility is also used by IT professionals for secure file deletion, but attackers can misuse it after they gain network access.
ESET attributed the initial break-in to UAC-0099, a Russia-linked group it said specializes in network access. The firm assessed that UAC-0099 handed access to Sandworm and said the destructive activity bore signs associated with Sandworm, Reuters reported. ESET could not determine which group operated the backdoor during the period between the initial breach and data wipe.
Reuters described Sandworm as associated with Russian military intelligence and noted prior blame for attacks on power systems in Ukraine and Poland. ESET declined to name the victim and could not determine the affected computers’ purpose or confirm that the incident disrupted grain operations.